
Resource Tags
Organization-wide labels that classify resources and keep a growing library organized and navigable.
Defining an organization's resource tags and choosing which resource types each one applies to are organization-level administrative actions, carried out in Organization Settings. What you can view and change depends on the role permissions you have been granted. The access model is documented in one place: Access & Permissions.
Overview
A resource tag is a label your organization defines for itself and applies to its resources — the things people and agents build in Opal, such as agents, skills, flows, templates, guardrails, tools, and widgets. Tags answer a question that gets harder as an organization grows: which of these belong together?
Two characteristics make them useful:
- They are organization-wide. Tags are defined once, at organization level, so everyone classifies resources with the same shared vocabulary instead of inventing personal labels.
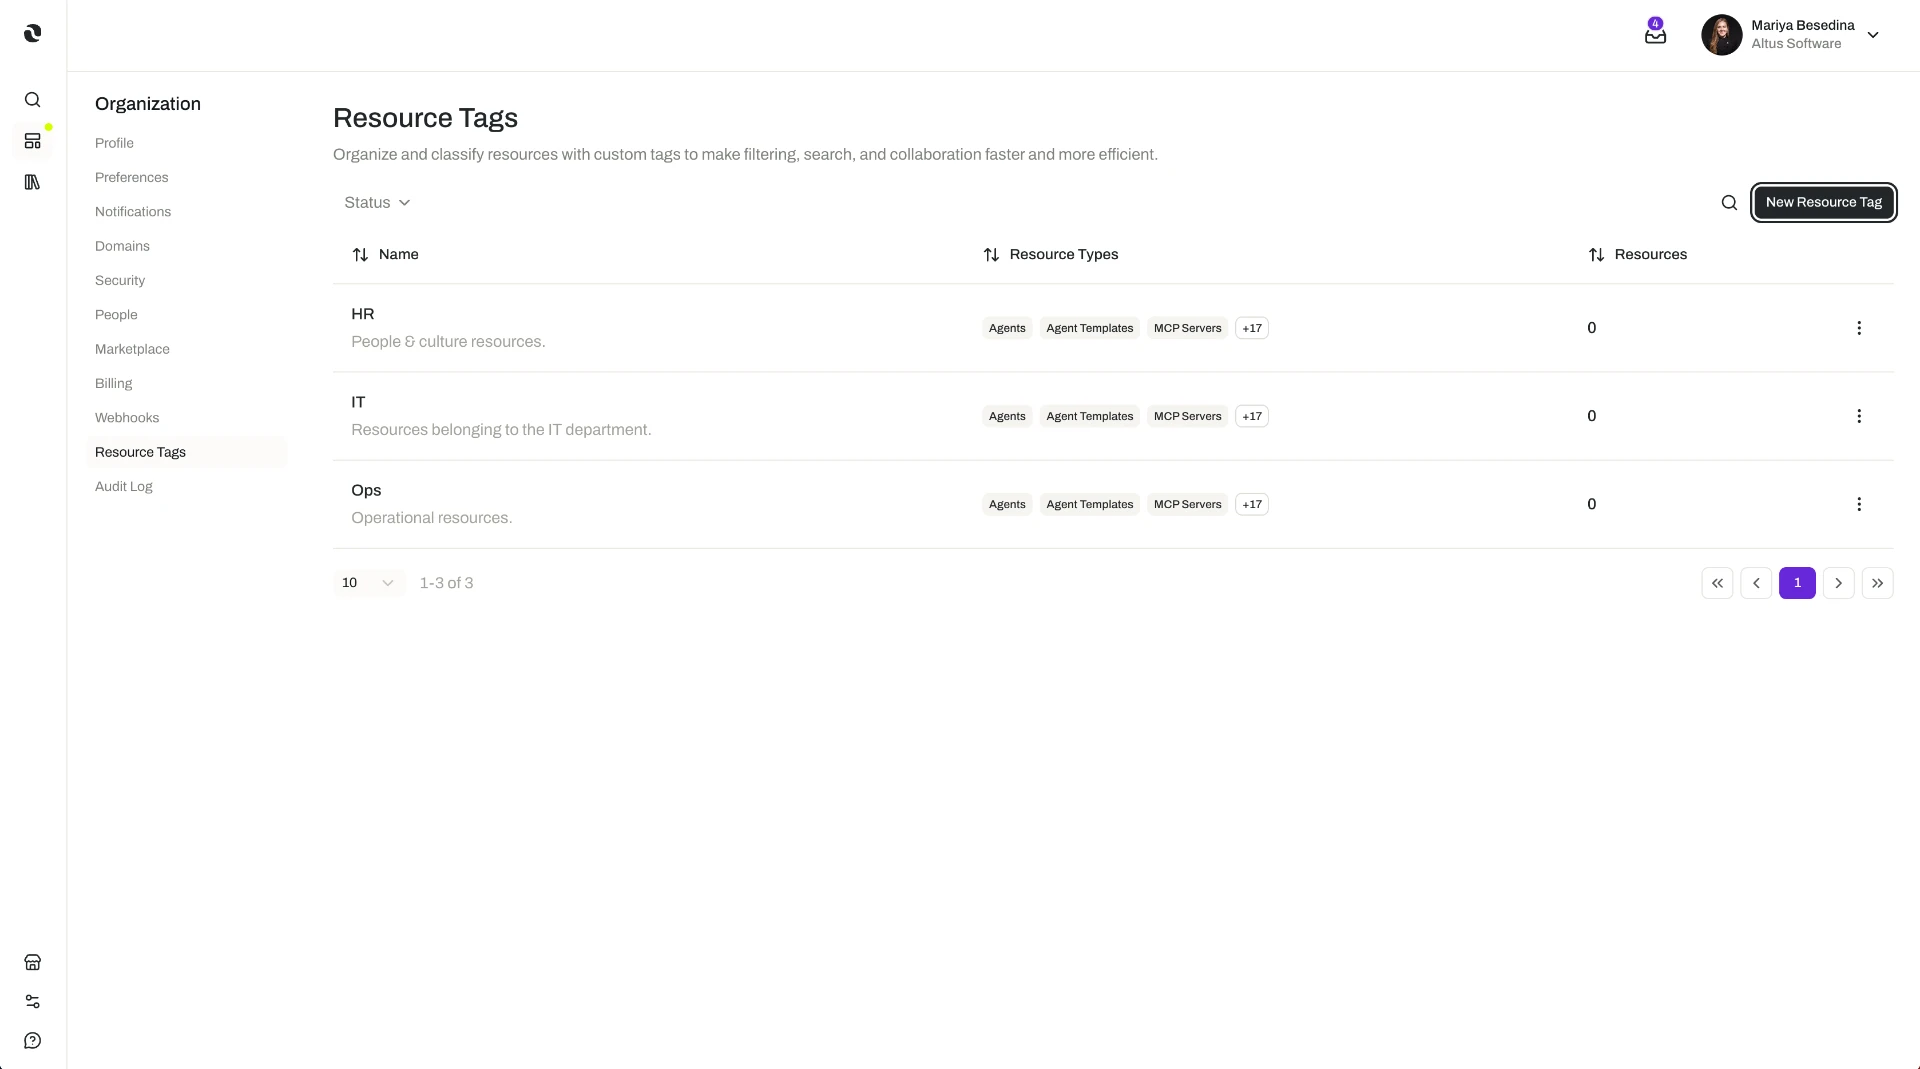
- They are a way to look at your resources, not just to label them. From the Resource Tags section of Organization Settings, members can view all resources that carry a given tag — so a tag becomes a live view of a group of resources.
Each tag also specifies which resource types it can be applied to, which keeps tags meaningful: a tag intended for customer-facing agents doesn't clutter the options on unrelated resource types.
Tagging is one of Opal's governance controls, and governance in Opal is a cross-cutting layer of trust and control rather than something added after the fact. Permissions decide who can do what, versioning keeps changes safe, the activity log records what happened — and tags keep a growing library organized and navigable so that oversight stays practical at scale.
A typical example: an organization defines a Production-Critical tag, applies it to the resources that keep production running, and then uses the Resource Tags section to review that whole group at once whenever something needs checking.
Key Capabilities
- Define organization-wide tags. An organization creates its own tags, so the classification scheme reflects how that organization actually works.
- Choose which resource types each tag can be applied to. Every tag specifies the resource types it is available on.
- Classify resources consistently. Because tags are defined centrally, teams label resources with a shared vocabulary rather than one of their own.
- Filter to everything carrying a tag. From the Resource Tags section of Organization Settings, members can view all resources that share a given tag.
- Keep a growing library navigable. Tags give teams a way to keep a large and expanding set of resources organized and easy to move around in.
- Administer tags alongside everything else. Resource tags sit in Organization Settings with the organization's profile and preferences, security, membership, teams and roles, billing, and credits — one place for organization administration.
How it Works
Tags belong to the organization. Resource tags are defined and managed at organization level, in the Resource Tags section of Organization Settings. That is what makes them shared: the same set of tags is available to everyone, rather than each team maintaining its own labels.
Each tag declares the resource types it can be applied to. When a tag is defined, the organization sets which resource types it covers. A tag is then available on resources of those types, and not on others.
Creating and applying a tag, in order.
- In Organization Settings, open the Resource Tags section.
- Create a tag with the label your organization wants to use — the wording everyone will recognize, such as Production-Critical or Finance.
- Choose the resource types the tag can be applied to.
- Apply the tag to individual resources of those types as people build and review them.
- Come back to the Resource Tags section to view all resources carrying that tag.
Filtering is what turns a label into oversight. The Resource Tags section is not only where tags are defined; it is also where they are used. Selecting a tag shows every resource that carries it, which makes group-level questions answerable in one place — what do we have that reaches customers?, which resources does this initiative depend on?
Tags work alongside the other governance controls. Opal's governance controls follow a common model across resources — sharing and permission levels, draft-and-publish versioning, version history, the activity log, linked resources, the optional publishing workflow, and tagging. Not every resource supports every control, so the controls available depend on the resource you are looking at. Tags complement the others: permissions govern access, versioning governs change, and tags govern how you find and group things.
A worked example. A compliance lead is responsible for a library of resources that keeps growing, and needs to keep an eye on the ones that production depends on. Rather than tracking them in a separate list, she defines a Production-Critical tag in Organization Settings, sets it to apply to the resource types those production-critical resources belong to, and asks builders to apply it as they publish. From then on, reviewing that group is a single step: she opens the Resource Tags section, selects the tag, and sees everything carrying it — including anything added since her last review.
A practical habit, not a product rule: a small, agreed set of tags is easier to keep accurate than a large set of overlapping ones. Deciding what each tag means before rolling it out is what keeps the filtered view trustworthy later.
Additional Notes
- Tags classify; they do not grant access. Applying a tag does not change who can open, edit, or use a resource. Access comes from sharing and permission levels and from role-based access control, which are documented separately: Governance and Access & Permissions.
- A tag only appears where it was set up to appear. Because each tag specifies its resource types, you will not see a tag offered on a resource type it was not defined for.
- Governance controls vary by resource. Opal applies a consistent governance model across resources, but not every resource supports every control — so check the resource itself for which controls are available.
- Some details are not documented here. Tag limits, color or styling options, naming rules, and exactly where the tag control appears on each resource type are not covered in this documentation. Check the Resource Tags section of Organization Settings for what applies to your organization.
- Organization-wide, not per space or per person. Resource tags are an organization-level setting. They are not a personal label and not scoped to an individual space.
- Short definitions of the terms used here are in one place: Glossary.
Related Features
- Governance — The full set of controls tags belong to: permissions and sharing, versioning, the activity log, linked resources, and the publishing workflow. Governance
- Platform Configuration — The cluster this page belongs to: the organization-wide configuration options, including resource tags, variables, and webhooks. Platform Configuration
- Variables — Organization-level values that configuration and integrations draw on, managed alongside tags in Organization Settings. Variables
- Webhooks — How an organization subscribes to platform events and sends them to external systems. Webhooks
- Access & Permissions — The full access model behind plans, role permissions, and per-resource permissions. Access & Permissions
- Glossary — Short definitions of the resource and governance terms used on this page. Glossary